TL;DR
Maersk said on November 11 that someone accessed and extracted data from a local legacy system inherited through a previous acquisition. The company says its investigation is ongoing and that it has found no sign of wider system impact or expected disruption; a ransomware group’s reported 100 GB theft and $5 million demand remain unverified.
A.P. Moller–Maersk said November 11 that an intruder accessed and extracted data from a local legacy system inherited through a previous acquisition. The shipping and logistics company says its investigation is ongoing, with no indication so far of effects on other Maersk systems or customer connections; a ransomware group’s reported theft and ransom claims have not been confirmed by Maersk.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
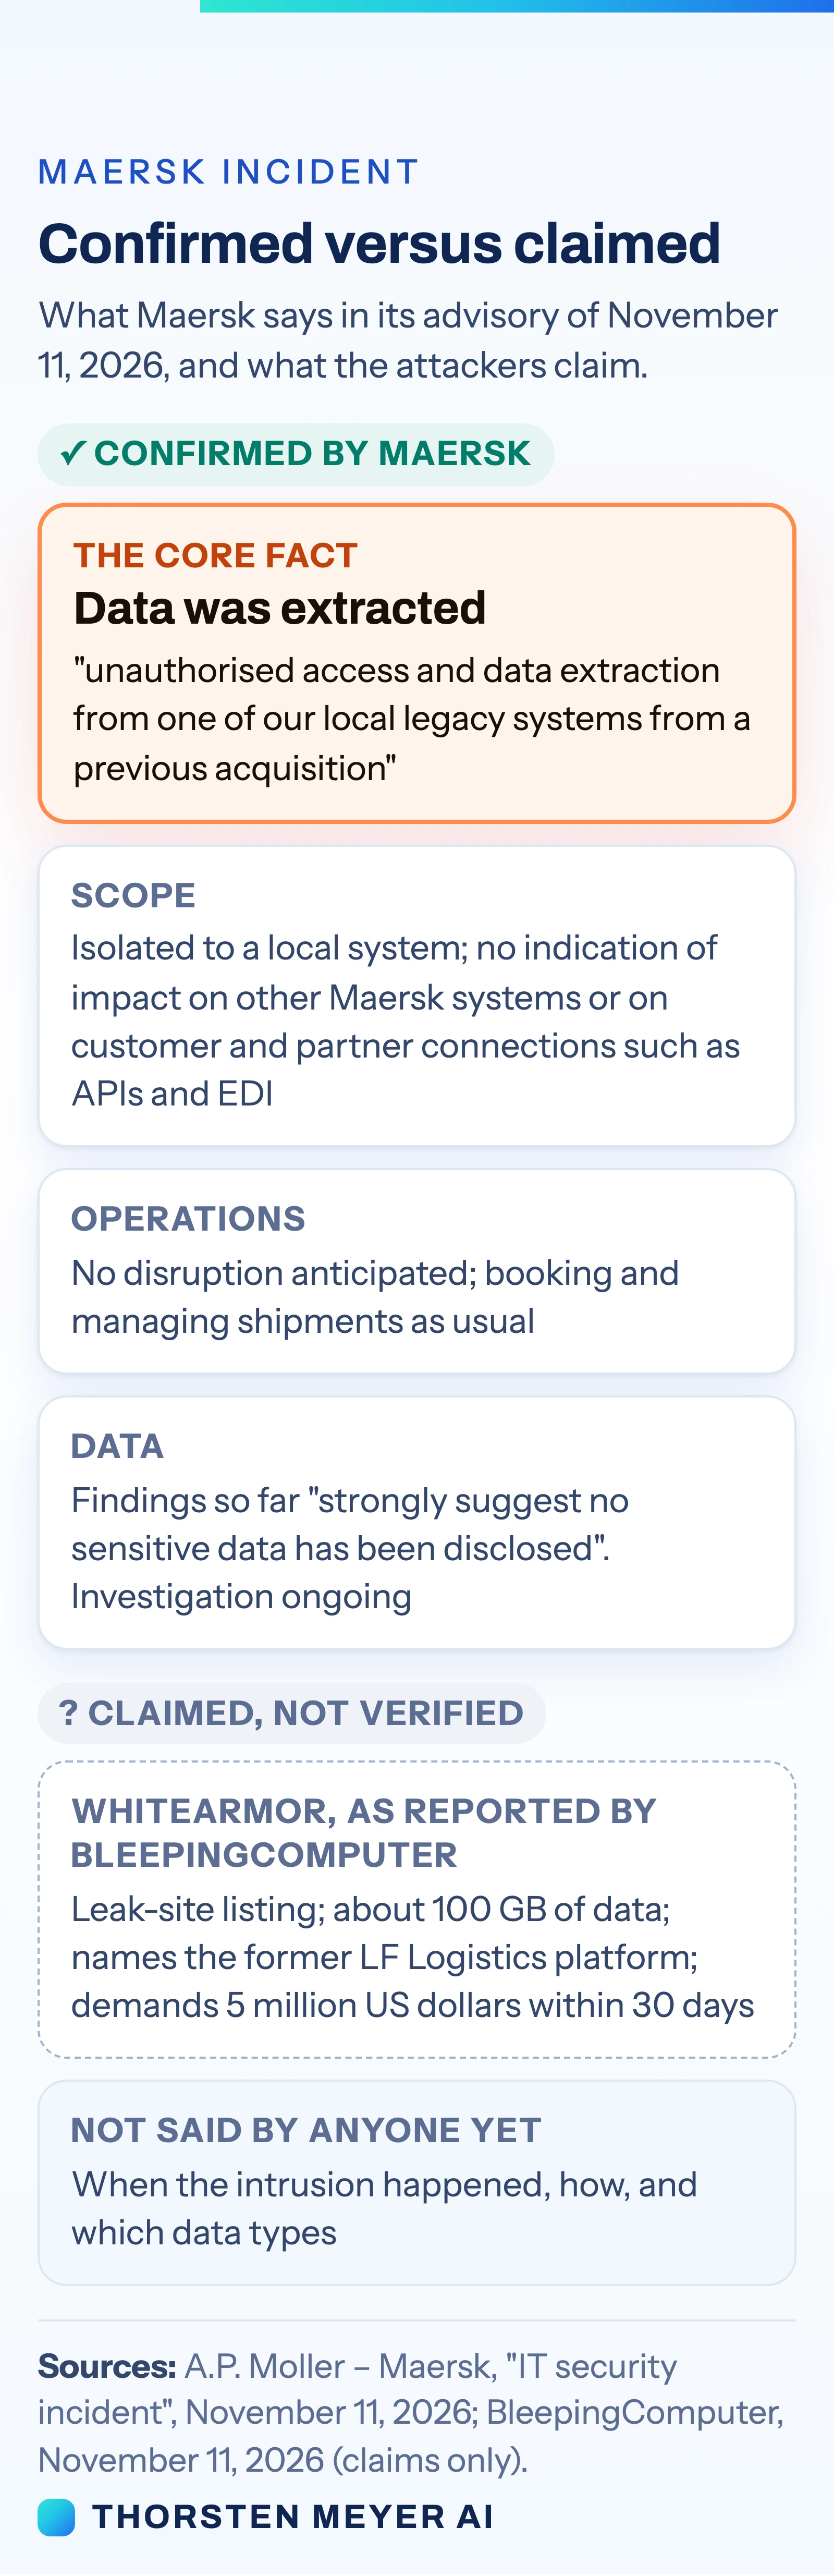
In an advisory titled “IT security incident,” Maersk said its cybersecurity team discovered the issue and launched a full investigation, taking steps to secure the affected system. The company said its findings so far “strongly suggest no sensitive data has been disclosed.” It did not define “sensitive” or explain what it means by “disclosed.” The statement confirms data extraction, but does not specify what data was taken or who accessed it.
Maersk described the incident as isolated to a local system and said it had found no indication of impact on other company systems or on customer and partner systems connected through integrations such as APIs and EDI. It said it did not anticipate disruption to customer operations at the time of the advisory, and that customers could continue using its platforms to book and manage shipments as usual.
BleepingComputer reported that a ransomware group called WhiteArmor listed Maersk on a leak site and claimed it had about 100 GB of data. The publication reported a $5 million ransom demand and a 30-day deadline. Those are the group’s claims as reported by BleepingComputer; Maersk’s advisory does not name WhiteArmor, mention a ransom, or confirm the amount or nature of the alleged data.
What the Incident Means for Shippers
For customers, the immediate operational guidance from Maersk is to continue using its booking and shipment-management platforms. The company says it has found no indication that the incident reached systems connected through APIs or EDI, which businesses use to exchange information with logistics providers. That is a statement about findings so far, while the investigation remains open.
The data question matters beyond immediate service continuity. Maersk has confirmed extraction, but has not described the records involved or whether any have been published, accessed by others, or used. Businesses receiving unexpected messages purporting to relate to the incident could face confusion or impersonation attempts. Maersk advises customers to treat such communications with caution and verify them through their usual company contact.
The reported ransom demand may attract attention, but it does not establish that the attackers possess the volume or type of information they claim. Until Maersk or further reliable reporting establishes more, the operational status and the attackers’ allegations should be treated as separate issues.
Products Worth Considering

Anker SOLIX C1000 Gen 2 Portable Power Station with 200W Solar Panel

LG UltraGear 32-inch Curved QHD Gaming Monitor (2560×1440, 180Hz, 1ms, 1000R, HDR10)

Bose TV Speaker Compact Soundbar with Bluetooth and HDMI-ARC, Black
As an affiliate, we earn on qualifying purchases.
The Acquisition Behind the Legacy System
Maersk has not identified the acquisition or system involved. The company’s wording only says the affected system came from “a previous acquisition.” BleepingComputer reported that WhiteArmor described the system as the “OCF/LF Logistics platform,” but that connection remains an attacker claim, not a detail confirmed by Maersk.
Maersk completed its acquisition of LF Logistics on August 31, 2022. At the time, it described the Hong Kong-based company as providing contract logistics, omnichannel fulfilment, e-commerce and inland transport services in the Asia-Pacific region. Maersk said the deal added 223 warehouses, bringing its global facility total to 549, and that LF Logistics employed 10,000 people. Those figures describe the scale of that acquisition; they do not establish that its systems were involved in this incident.
The distinction matters because large acquisitions can leave businesses operating systems inherited from the acquired company. In this case, however, the available information does not identify which legacy environment was accessed or establish how it was connected to Maersk’s broader network.
“Our findings so far strongly suggest no sensitive data has been disclosed.”
— A.P. Moller–Maersk, November 11 advisory
The Data and Intrusion Remain Unspecified
Maersk has not named the affected system, the acquisition it came from, or when the unauthorized access occurred. It has also not identified the data types extracted or explained the scope of its assessment that no sensitive data has been disclosed. The company says its investigation is ongoing.
It remains unclear whether WhiteArmor’s reported claims are accurate, whether the alleged 100 GB refers to data actually taken from Maersk, and whether any information has been published or shared. Maersk’s advisory does not confirm the group’s identity, the alleged link to LF Logistics, or the reported ransom demand. BleepingComputer said it had asked Maersk for further details and had not received a response by publication.
Maersk to Update Affected Parties
Maersk said it would update customers as relevant information becomes available and inform impacted parties if it determines that this is necessary. Its cybersecurity investigation and work to secure the affected system are continuing. The company has not provided a timetable for further findings.
Customers should continue to use Maersk’s platforms as advised in the notice and verify unexpected communications about the incident through their usual Maersk contact. Further clarity depends on the company’s investigation and any substantiated information about the attackers’ claims.
Key Questions
What did Maersk confirm?
Maersk confirmed unauthorized access and data extraction from a local legacy system inherited through a previous acquisition. Its investigation is ongoing.
Did Maersk confirm a $5 million ransom demand?
No. BleepingComputer reported that WhiteArmor demanded $5 million, but Maersk’s advisory does not mention a ransom or confirm the group’s claim.
Were customer systems or shipments affected?
Maersk said it had found no indication of impact on other company systems or customer and partner connections such as APIs and EDI. It did not anticipate operational disruption at the time of its advisory and said customers could keep using its platforms.
Was LF Logistics the acquired business involved?
That has not been confirmed. WhiteArmor reportedly named an OCF/LF Logistics platform, but Maersk has not identified the acquisition or system involved.
What should Maersk customers do?
Maersk advises customers to treat unexpected communications claiming to relate to the incident with caution and verify them through their usual Maersk contact.
Source: Thorsten Meyer AI